IAM-04 / Identity Governance

Governed Finance Access Lifecycle

Designed and validated an end-to-end Microsoft Entra Identity Governance workflow for sensitive Finance access. The solution governs access from business request and approval through automated provisioning, periodic certification, denial, and automatic revocation.

30 Days
Time-bound assignment
1 Stage
Business approval
Monthly
Access review cadence
Automatic
Governance revocation
Video Walkthrough · 2–3 min

See the project in action

A concise walkthrough of the architecture, Microsoft Entra configuration, controls, and validation evidence behind this project.

Open on YouTube ↗
01 / Challenge

Sensitive access should have a lifecycle, not just an approval.

Autumn Solutions needed a governed method for granting temporary Finance access without relying on permanent group membership or manual administrator cleanup. The control needed to capture business justification, separate the requester from the approver, provision access automatically, periodically recertify the assignment, and remove access when it was no longer required.
02 / Design

Microsoft Entra Entitlement Management as the governance layer.

I created a Finance access catalog and access package containing SG-Finance and the LedgerFlow enterprise application. Taylor Brooks could request the package, while Jordan Lee served as the business approver and recurring access reviewer.

Microsoft Entra ID Identity Governance Entitlement Management Access Packages Approval Workflows Access Reviews Least Privilege
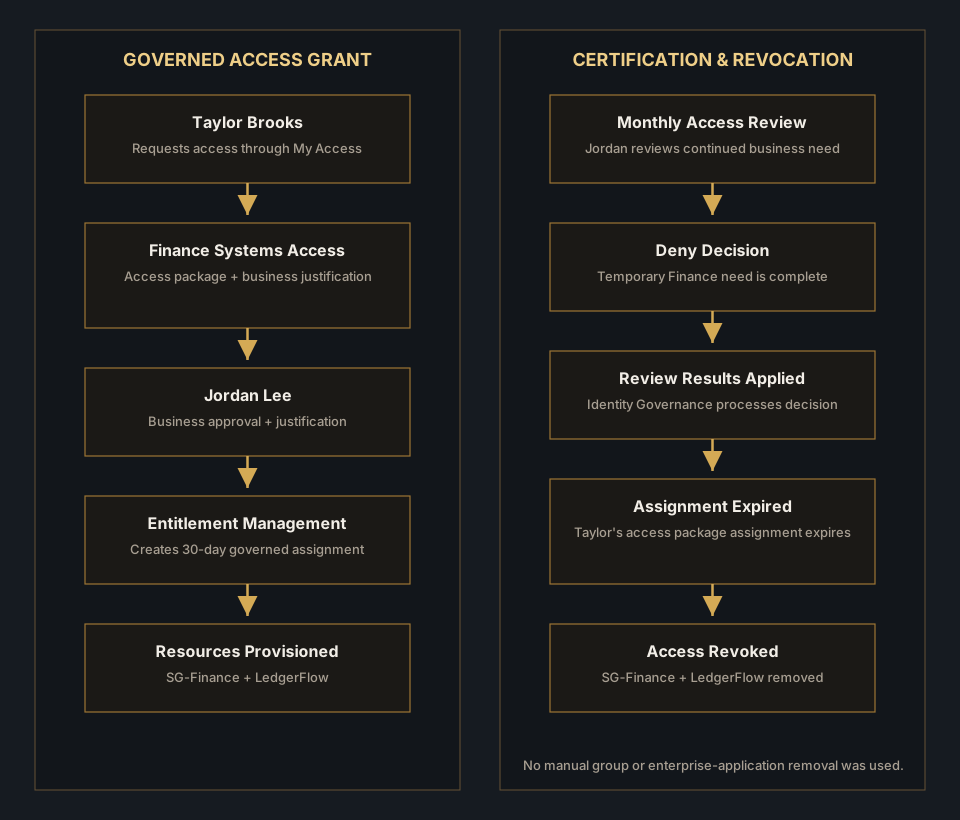
IAM-04 Microsoft Entra Identity Governance lifecycle showing access request, approval, entitlement provisioning, access review, denial, and automatic revocation
03 / Lifecycle

Request to revocation without manual access cleanup.

01

Request

Taylor requested Finance access and supplied the required business-process answer and justification.

02

Approve & Provision

Jordan approved the request. Entitlement Management then provisioned SG-Finance membership and LedgerFlow access automatically.

03

Review & Deny

The scheduled recurring review activated automatically. Jordan determined that the temporary business need had ended and denied continued access.

04

Apply & Revoke

Entra applied the review result, expired the governed assignment, removed Taylor from SG-Finance, and removed LedgerFlow access without a manual administrator removal.

04 / Evidence

Governance lifecycle evidence

The evidence below captures the business decision, active certification process, reviewer denial, applied results, and downstream revocation.

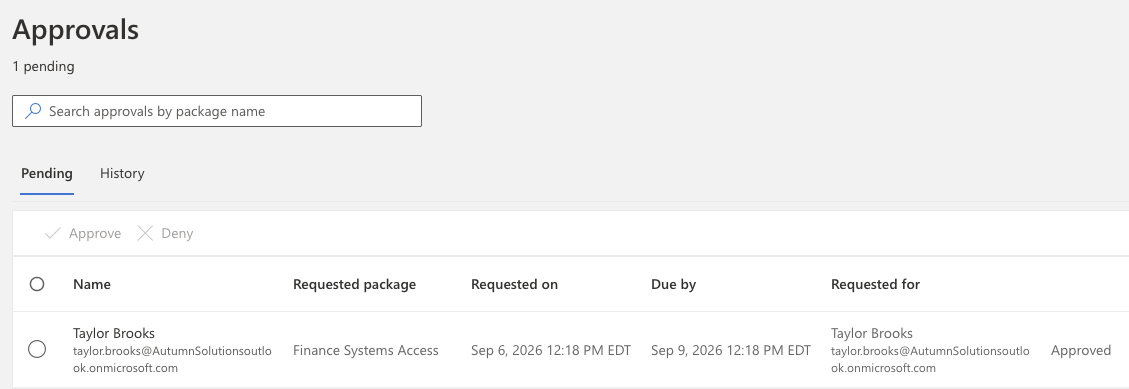
Jordan Lee approving the Finance access request
Business approval captured before access provisioning.
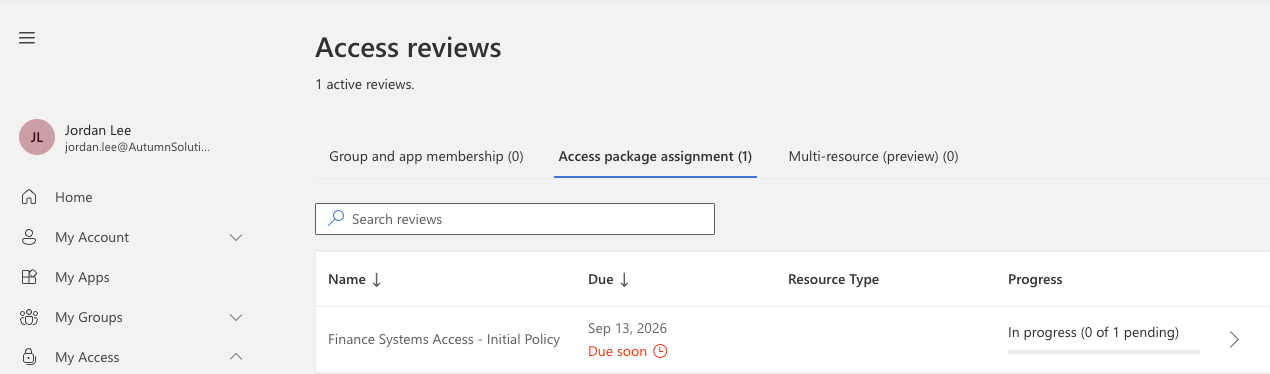
Active Microsoft Entra access review
Scheduled Finance access review automatically entered the active state.
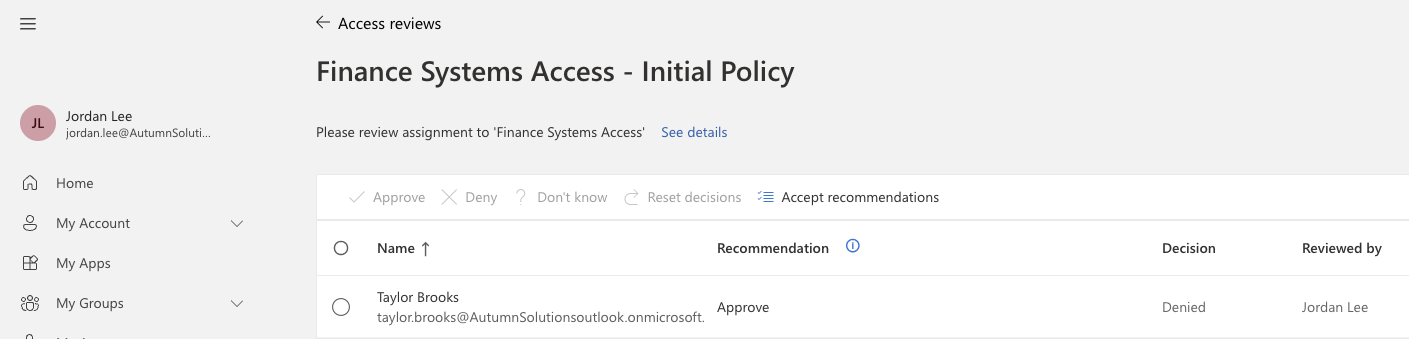
Jordan Lee denying Taylor Brooks continued access
Jordan denied continued access after the temporary business need ended.
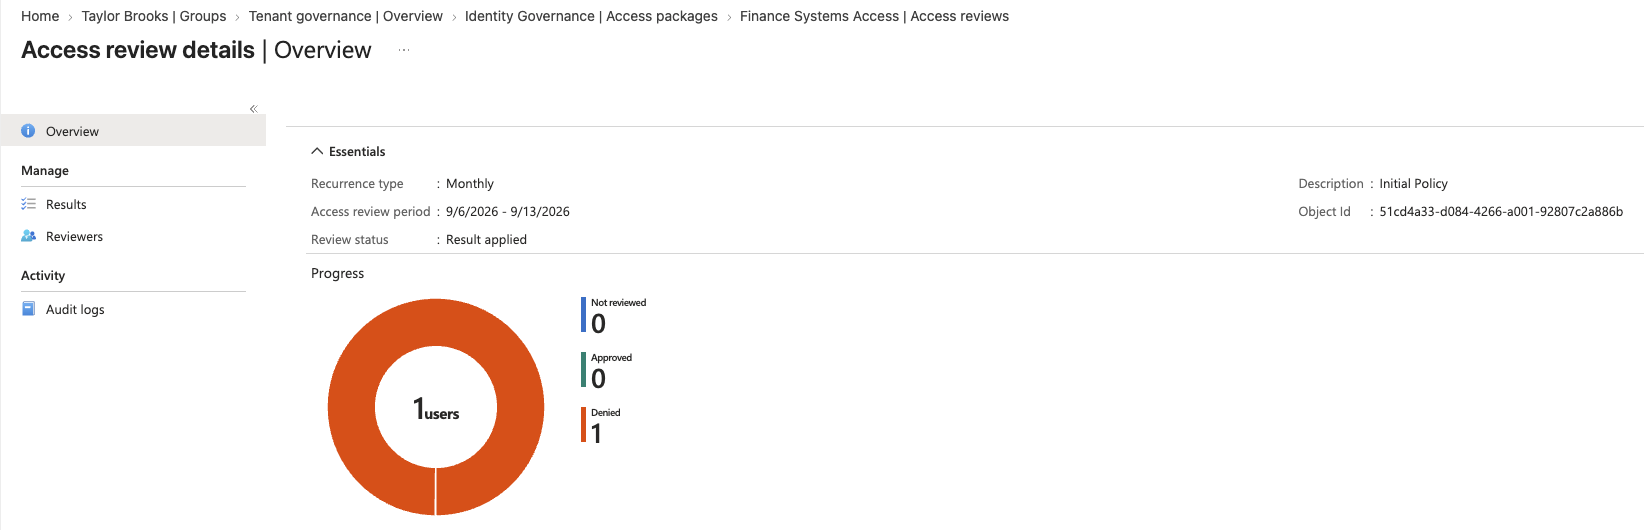
Microsoft Entra access review results applied
Entra completed the governance workflow and applied the review result.
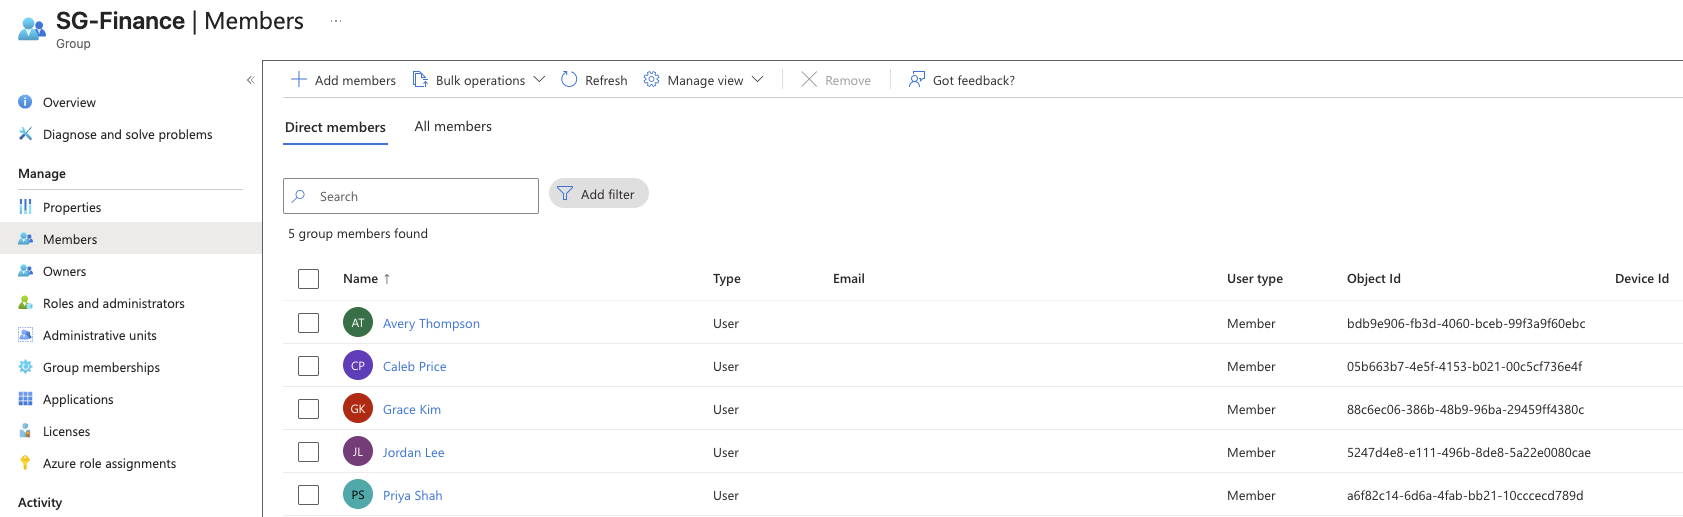
Taylor Brooks removed from SG-Finance
SG-Finance membership was revoked through the governance lifecycle.
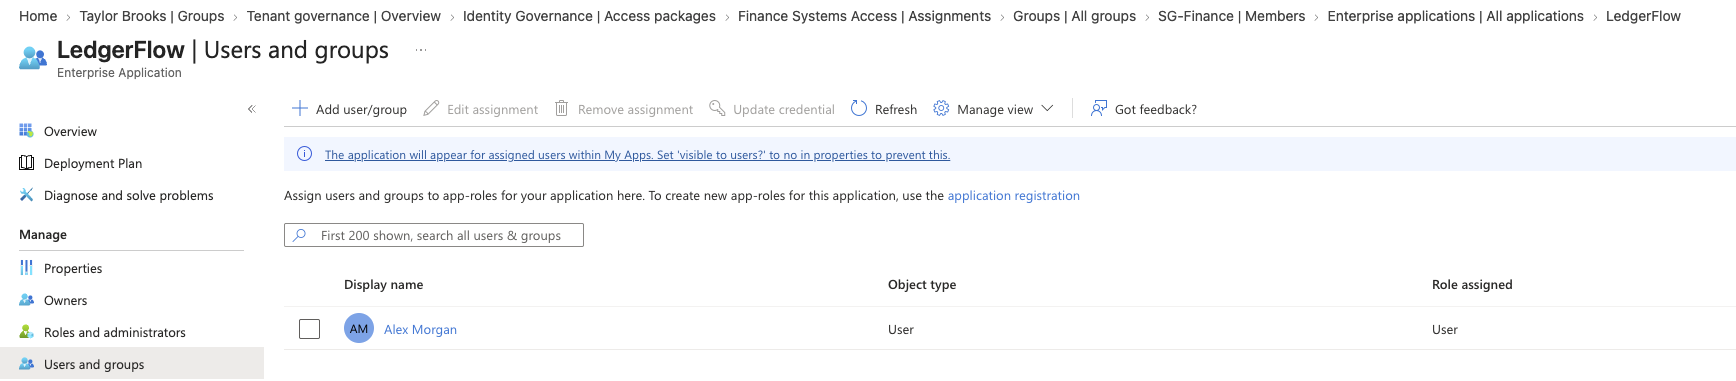
Taylor Brooks removed from LedgerFlow
LedgerFlow access was also removed after the review result was applied.
05 / Outcome

A complete governed access lifecycle.

The final implementation demonstrates that sensitive business access can be governed as a lifecycle rather than a one-time administrative action. Business justification was captured, approval responsibility was separated from IAM administration, access was provisioned automatically, continued need was recertified, and a Deny decision ultimately removed both group and application access automatically.

Key control outcome

No manual removal from SG-Finance or LedgerFlow was used to complete the revocation. The access review decision drove the governance lifecycle through expiration and downstream removal.