IAM-03 · Autumn Solutions

Identity Lifecycle Automation

I built an HR-driven Joiner, Mover, Leaver automation for Microsoft Entra ID. The workflow processes workforce events, manages identities, department access and licensing through Microsoft Graph, authenticates with an X.509 certificate, and records structured lifecycle audit evidence.

3
Lifecycle workflows
6
HR events validated
Graph
Identity control plane
X.509
Workload authentication
Video Walkthrough · 2–3 min

See the project in action

A concise walkthrough of the architecture, Microsoft Entra configuration, controls, and validation evidence behind this project.

Open on YouTube ↗
01 / Challenge

Turn HR lifecycle events into controlled identity changes.

Manual account creation, access changes, and offboarding create inconsistency and increase the chance of excessive or lingering access. Autumn Solutions needed a repeatable workflow that could translate HR events into Microsoft Entra identity actions while preserving auditability and least privilege.

Microsoft Entra ID Microsoft Graph Node.js Shell X.509 Certificates HR Automation JML Audit Logging
02 / Architecture

HR events drive the identity lifecycle.

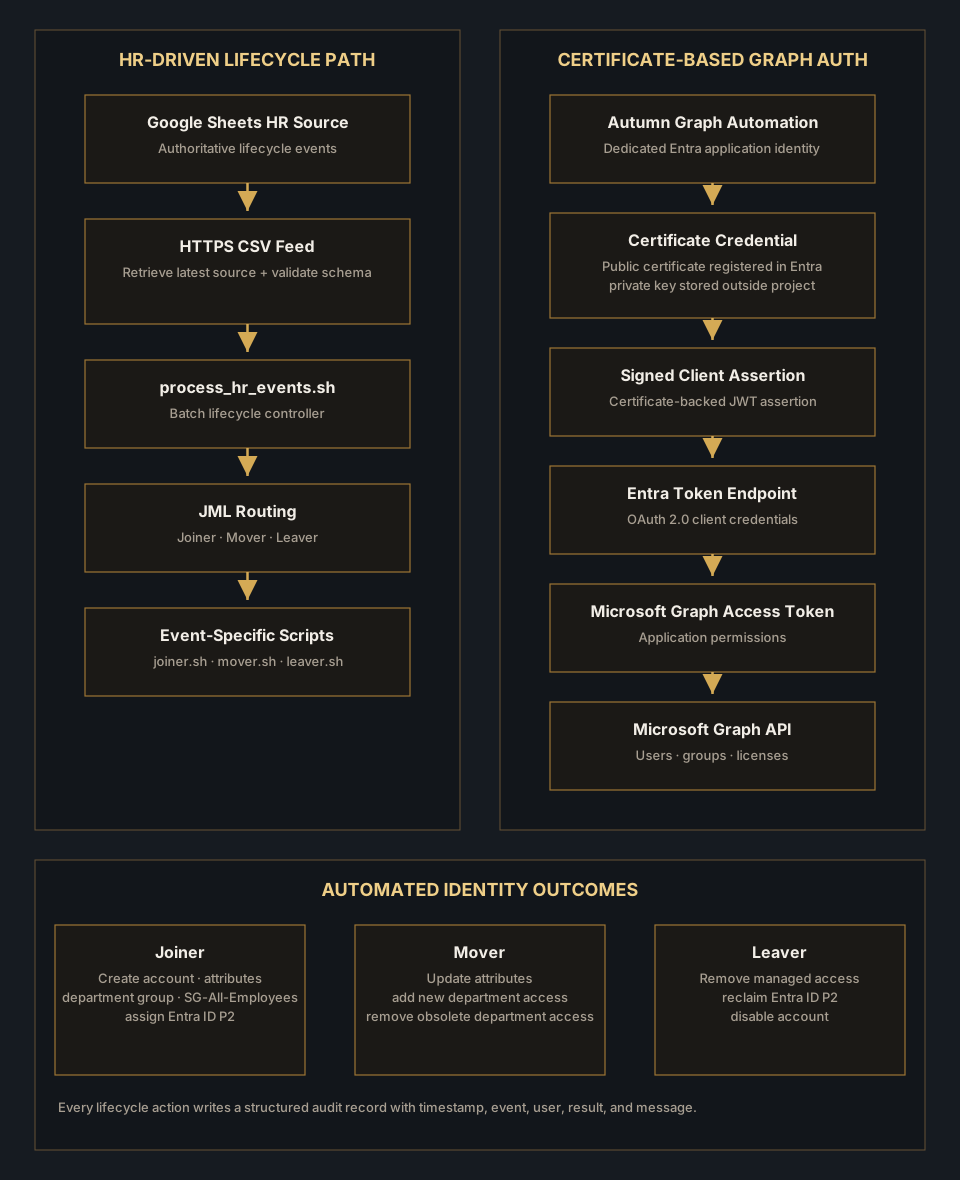
The automation separates the HR source, lifecycle decision logic, Microsoft Graph authentication, identity actions, and audit evidence. This keeps the workflow understandable and allows each Joiner, Mover, or Leaver event to be traced from source through execution.

IAM-03 HR-driven Joiner Mover Leaver architecture using certificate-based Microsoft Graph application authentication
03 / Lifecycle

Automated Joiner, Mover, and Leaver controls.

JOINER

Provision Identity

Creates the Entra identity, applies workforce attributes, assigns department access, adds the employee to the organization-wide group, and assigns the required license.

MOVER

Reconcile Access

Updates workforce attributes and changes department-based group access so authorization follows the employee's current business role instead of accumulating indefinitely.

LEAVER

Disable and Reclaim

Disables the user, removes managed access, and reclaims the assigned license so offboarding reduces both security exposure and unnecessary license consumption.

REPEAT

Idempotent Processing

Lifecycle processing was designed so repeated execution does not blindly recreate access or duplicate the same identity changes.

04 / Workload Security

Automation without embedding a reusable client secret.

The Microsoft Graph workload authenticates using an X.509 certificate and a signed client assertion. The private key is stored outside the project directory and is never committed with the automation source.

Certificate-Based Graph Authentication

The workload identity was separated from human administrator authentication and designed for non-interactive Graph access.

  • Dedicated Microsoft Entra application identity
  • X.509 certificate authentication
  • Signed client assertion
  • Private key stored outside the project
  • Application permissions scoped to lifecycle requirements
  • No credential material published in the repository
05 / Auditability

Lifecycle automation that leaves evidence behind.

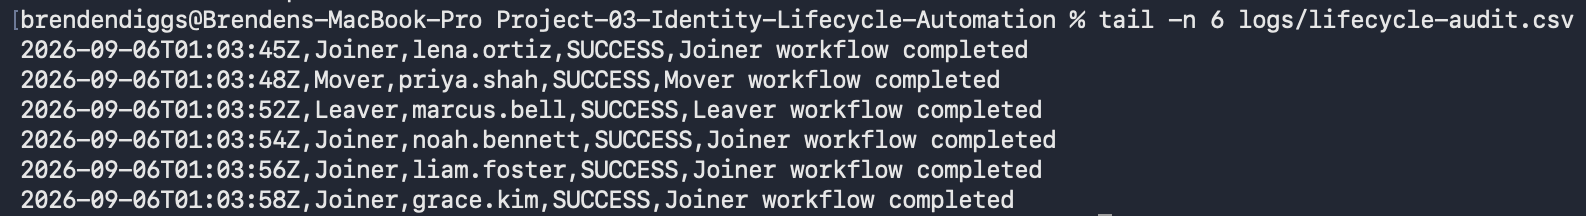
Automated identity changes are written to a structured lifecycle audit log. This creates evidence of which HR event was processed, which lifecycle action occurred, and the resulting identity change.

SOURCE

HR-Driven Events

Lifecycle actions originate from the HR source instead of being initiated as disconnected administrative changes.

LOG

Structured Audit Trail

Execution results are recorded in CSV format for troubleshooting, control validation, and portfolio evidence.

05 / Evidence

Identity lifecycle execution and validation.

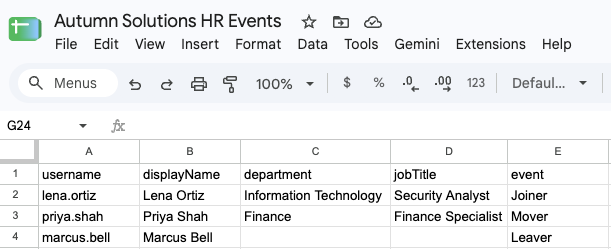
HR source feed used for identity lifecycle automation
HR source data driving Joiner, Mover, and Leaver lifecycle processing.
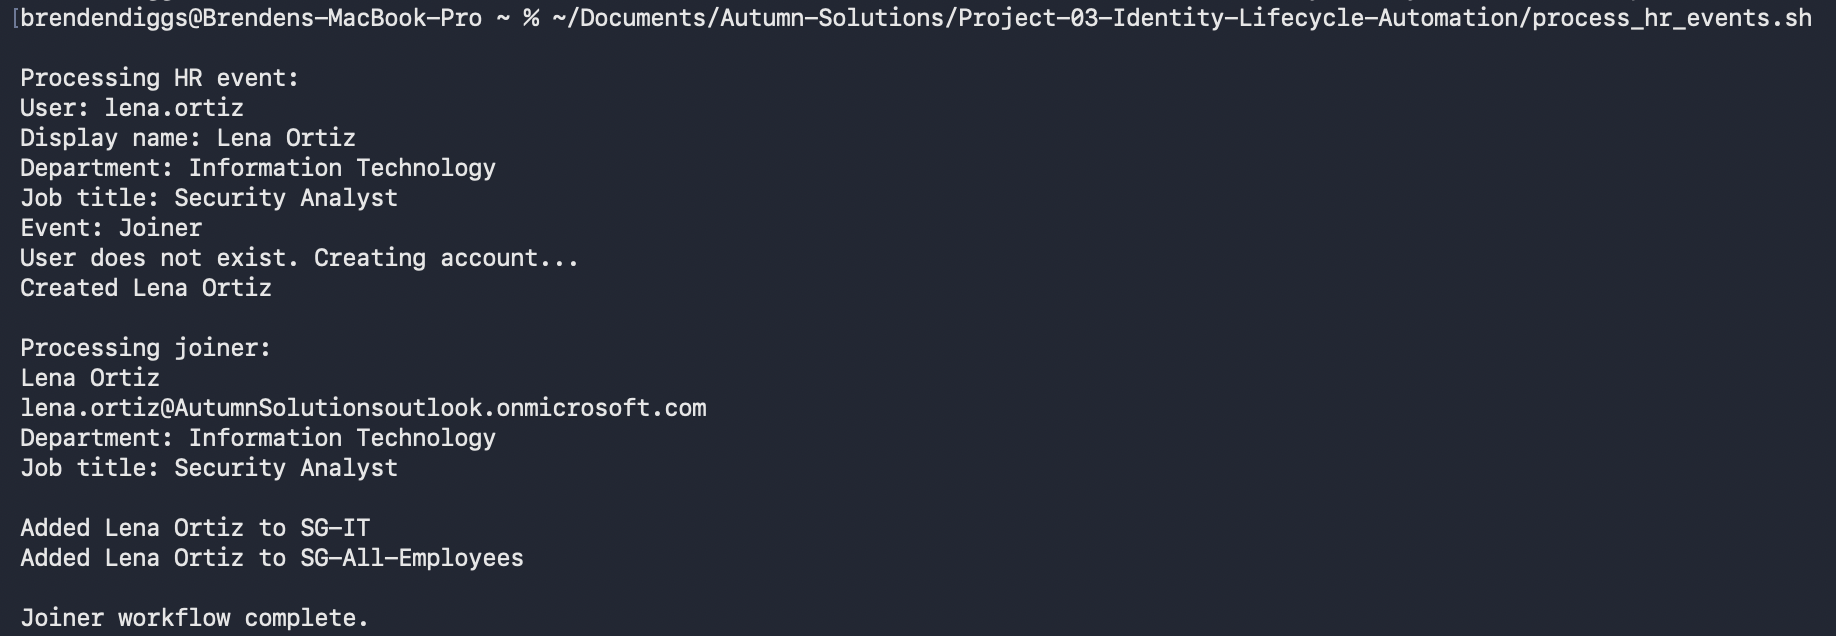
Successful automated Joiner workflow
Successful Joiner execution creating and configuring a new Entra workforce identity.
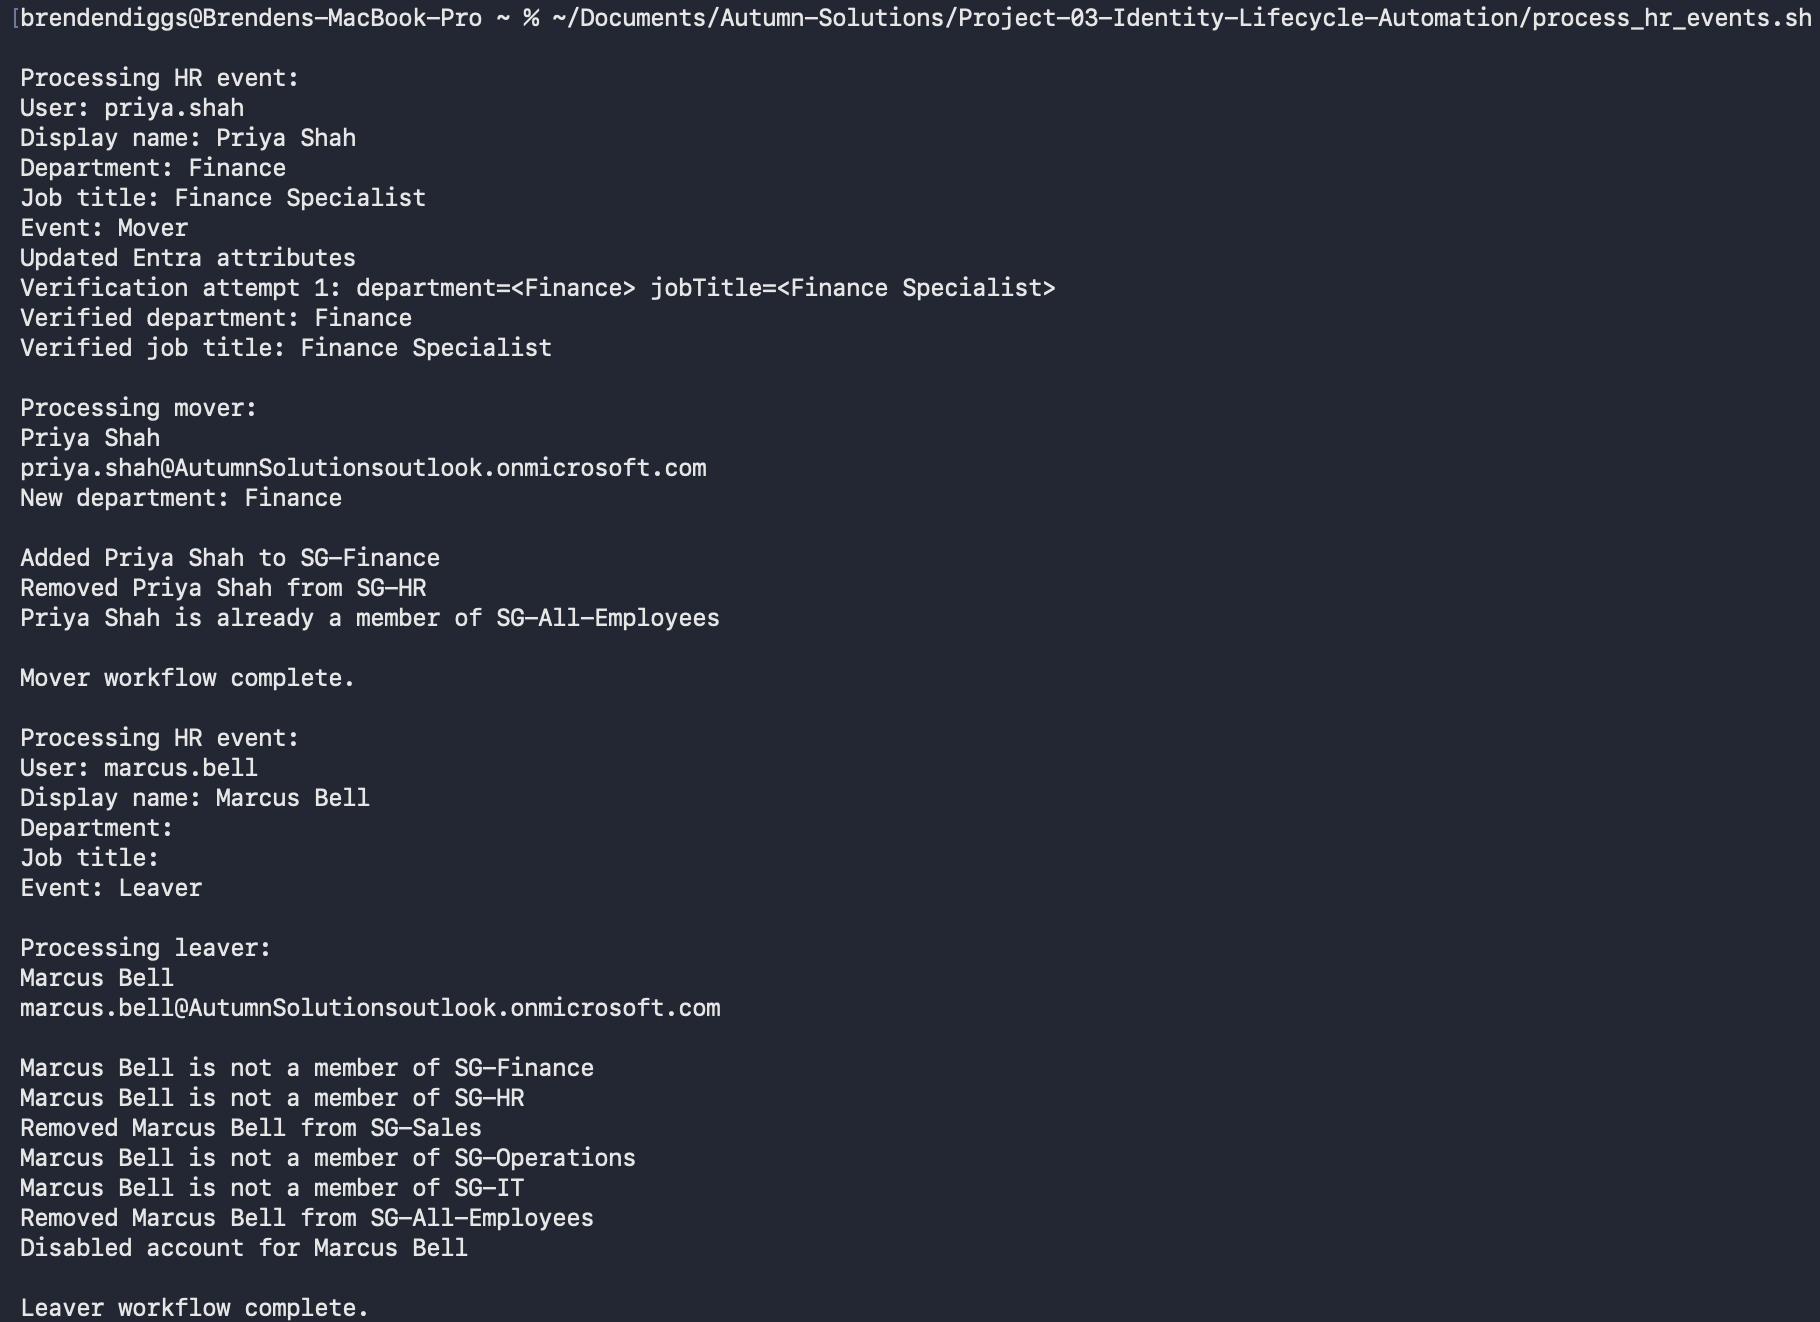
Successful automated Mover and Leaver workflows
Mover and Leaver execution validating automated access change, disablement, and lifecycle processing.
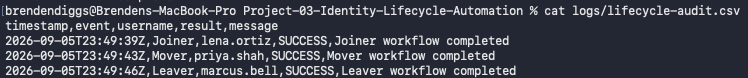
Structured identity lifecycle audit log
Structured audit evidence generated by the automated lifecycle workflow.
Certificate authenticated Microsoft Graph workload identity
Successful Microsoft Graph authentication using the dedicated certificate-based workload identity.
Certificate authenticated Joiner Mover Leaver automation success
End-to-end JML execution validated using certificate-authenticated Microsoft Graph access.
Outcome

HR events became auditable identity lifecycle actions.

IAM-03 connects identity engineering with business lifecycle events. Joiners receive the required identity, access, and license state; Movers have authorization reconciled as their role changes; and Leavers are disabled, stripped of managed access, and have licenses reclaimed. Microsoft Graph performs the identity changes while certificate-based authentication and structured logging strengthen the security and auditability of the automation itself.