IAM-02 · Autumn Solutions

Enterprise SSO & Federation

I built a multi-protocol enterprise identity integration for LedgerFlow, a fictional Autumn Solutions SaaS application. The solution demonstrates SAML 2.0 federation, OpenID Connect, OAuth 2.0 Authorization Code with PKCE, Microsoft Graph delegated access, and SCIM provisioning across one identity architecture.

SAML
Enterprise federation
OIDC
Modern authentication
OAuth
Delegated API access
SCIM
Lifecycle provisioning
Video Walkthrough · 2–3 min

See the project in action

A concise walkthrough of the architecture, Microsoft Entra configuration, controls, and validation evidence behind this project.

Open on YouTube ↗
01 / Challenge

Connect an enterprise SaaS application to the full identity lifecycle.

Autumn Solutions needed more than a simple sign-in demo. LedgerFlow had to support enterprise federation, modern web authentication, delegated Microsoft Graph access, custom identity claims, and automated account provisioning and deprovisioning.

Microsoft Entra ID SAML 2.0 OpenID Connect OAuth 2.0 PKCE Microsoft Graph SCIM 2.0 Node.js
02 / Architecture

One application, multiple enterprise identity protocols.

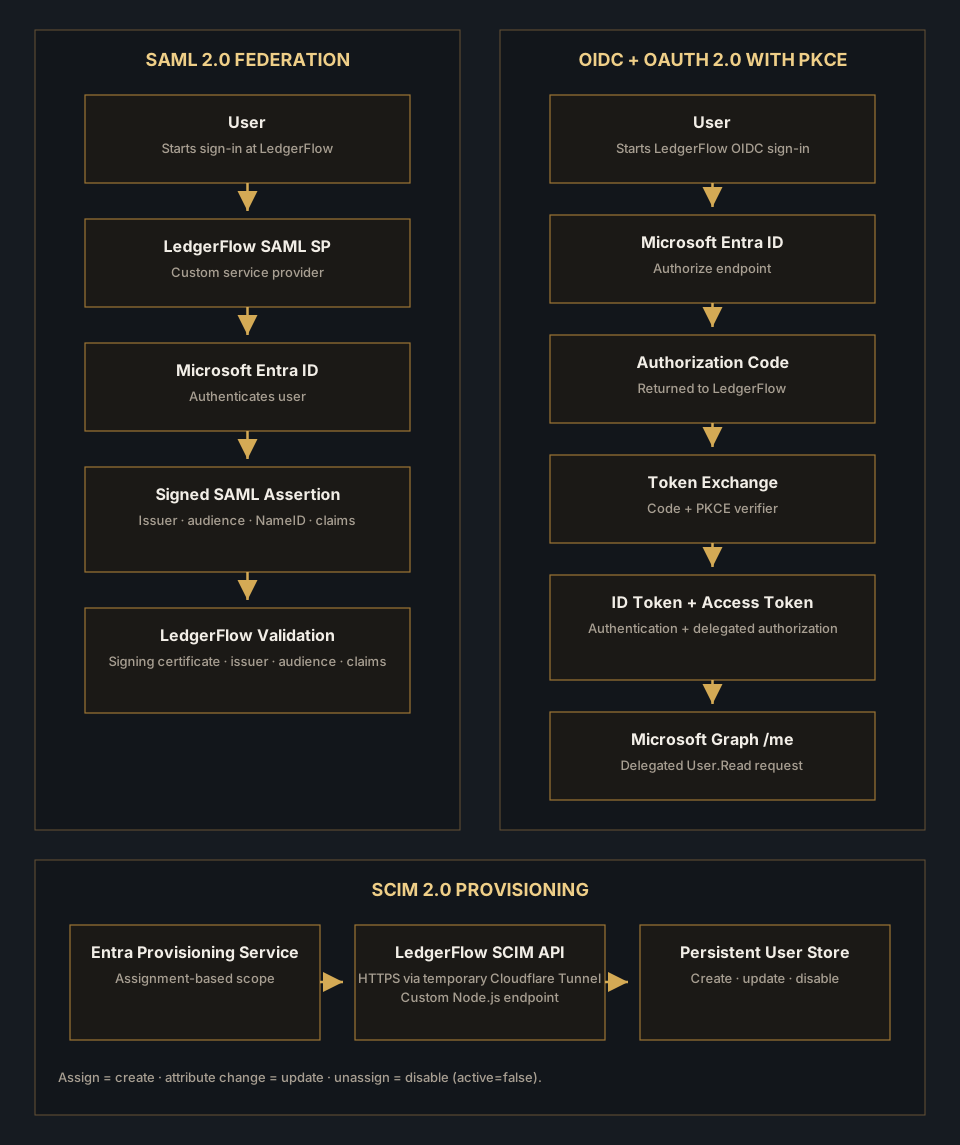
Microsoft Entra ID acts as the identity provider and authorization platform while LedgerFlow implements separate SAML, OIDC, and SCIM components. This demonstrates how authentication, authorization, claims, API access, and account lifecycle management fit together.

IAM-02 LedgerFlow identity architecture showing SAML federation, OIDC and OAuth 2.0 with PKCE, Microsoft Graph delegated access, and SCIM provisioning
03 / Federation

SAML federation with deliberate claim design.

01

Service Provider Configuration

Configured the LedgerFlow service provider and Microsoft Entra enterprise application with the required SAML identifiers, reply URL, sign-on configuration, and signing trust.

02

NameID & Claims

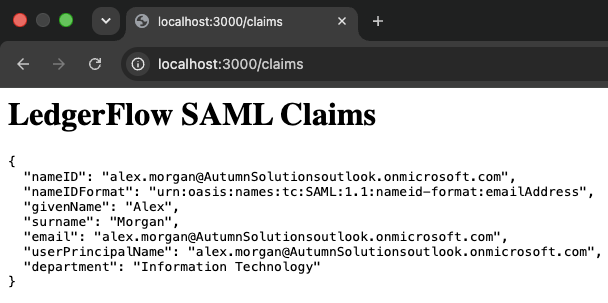
Configured the SAML NameID and added a custom department claim so LedgerFlow receives business-relevant identity attributes rather than authentication alone.

03

Group-Based Assignment

Controlled application access through Entra assignment instead of exposing the application indiscriminately to every tenant user.

04

Certificate Troubleshooting

Diagnosed a SAML validation failure to a stale signing certificate and restored federation by aligning LedgerFlow with the current Entra signing certificate.

04 / Modern Auth

OIDC authentication and OAuth delegated authorization.

A separate LedgerFlow OIDC application implemented modern user authentication through Microsoft Entra ID. The authorization flow used OAuth 2.0 Authorization Code with PKCE and obtained delegated Microsoft Graph access for the signed-in user.

Authentication vs Authorization

The project intentionally demonstrates the difference between proving who the user is and authorizing an application to access an API on that user's behalf.

  • OIDC ID token for authenticated identity claims
  • OAuth 2.0 authorization code flow
  • PKCE protection for the authorization exchange
  • Delegated Microsoft Graph access
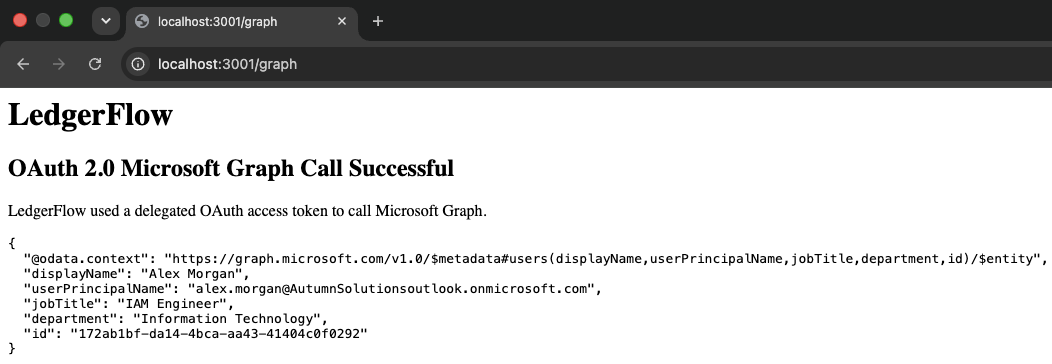
  • Successful Graph /me request
05 / Provisioning

SCIM connected access decisions to account lifecycle.

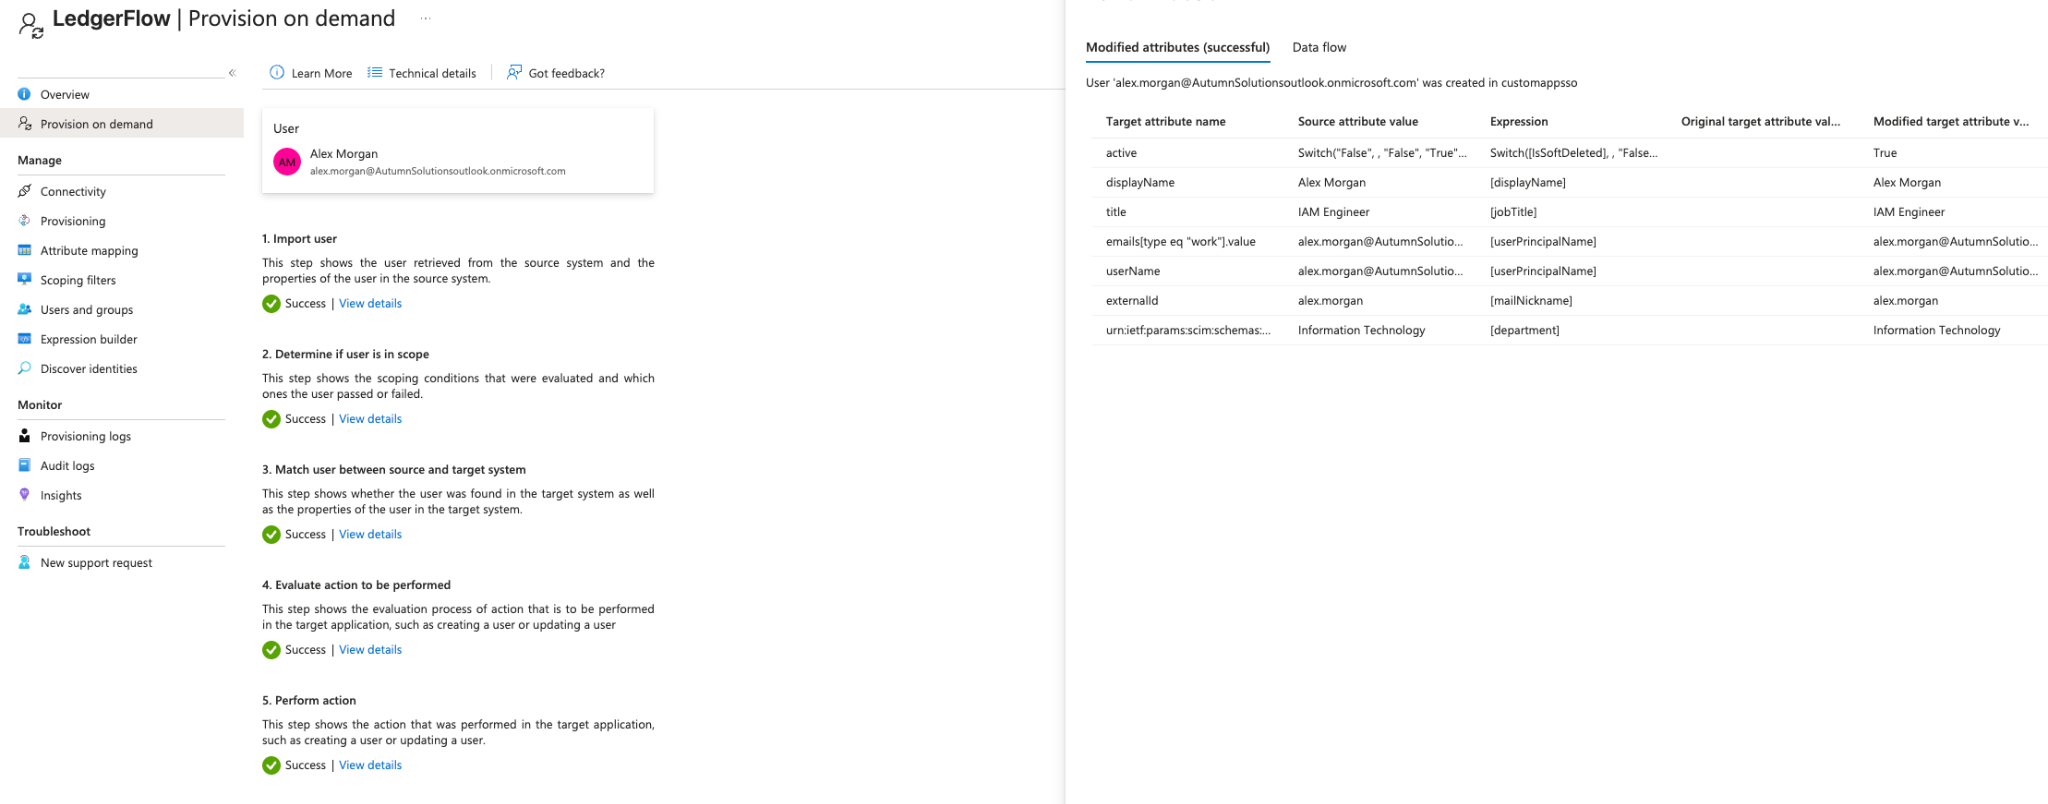
LedgerFlow's SCIM service receives lifecycle changes from Microsoft Entra provisioning. The workflow was validated across creation, persistent storage, attribute updates, and disablement.

CREATE

Provision User

Entra successfully created the target LedgerFlow identity through the SCIM service.

UPDATE

Synchronize Attributes

Identity attribute changes were propagated into the persistent LedgerFlow user store.

DISABLE

Deprovision Access

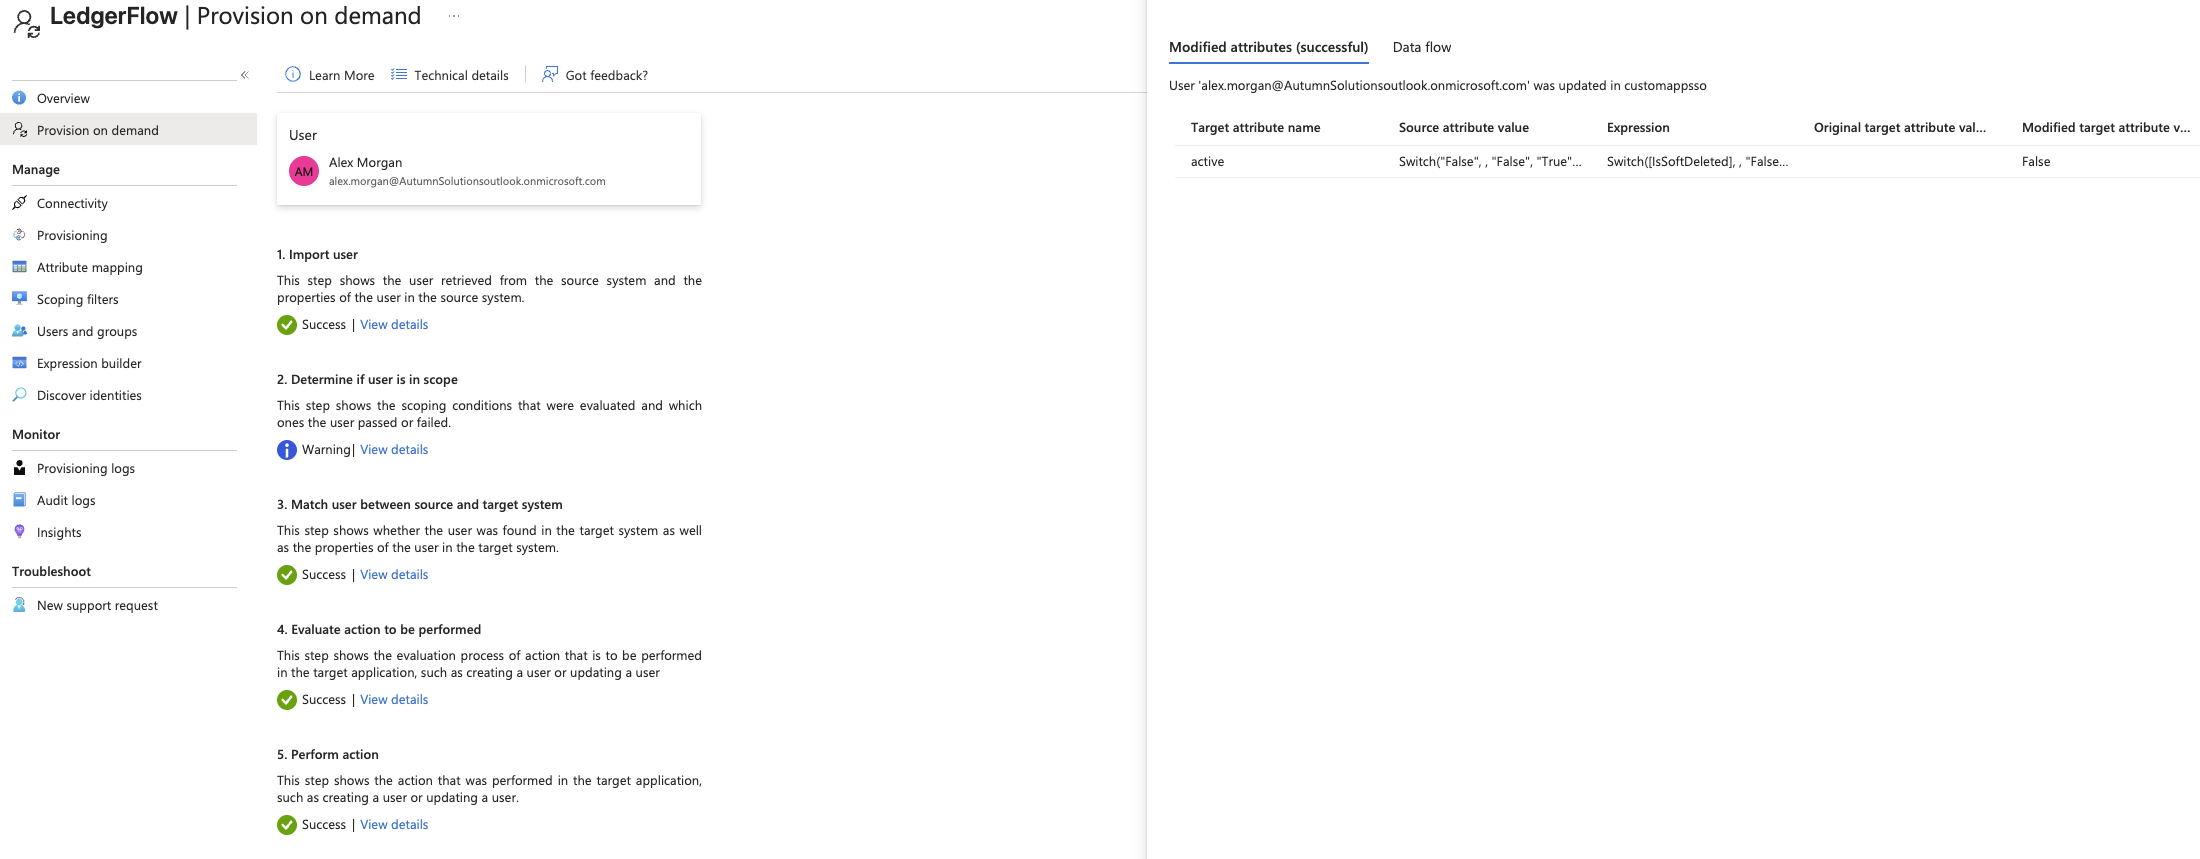
Removing the user from provisioning scope resulted in the LedgerFlow identity being disabled through the SCIM lifecycle.

VALIDATE

Troubleshoot Failures

Out-of-scope and target-write failures were investigated and corrected rather than bypassed, preserving evidence of the troubleshooting process.

05 / Evidence

Federation, authorization, and provisioning evidence.

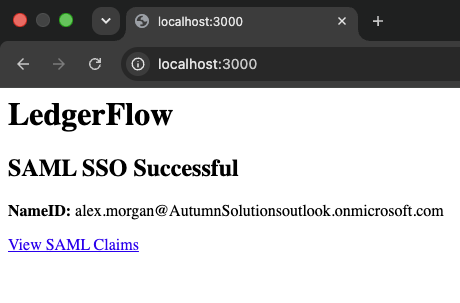
Successful custom LedgerFlow SAML single sign-on
Successful service-provider-initiated SAML authentication into the custom LedgerFlow application.
LedgerFlow SAML identity claims
LedgerFlow receiving the configured SAML identity claims after federation.
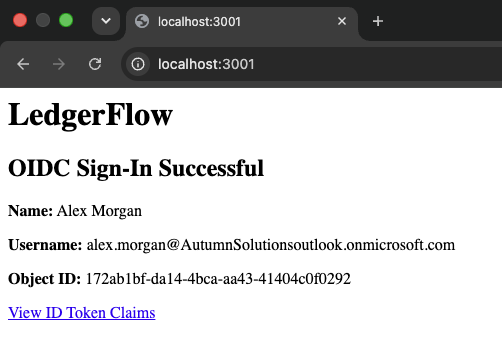
Successful LedgerFlow OpenID Connect sign in
Successful user authentication through the LedgerFlow OpenID Connect application.
Successful OAuth delegated Microsoft Graph access
OAuth delegated authorization successfully used to access Microsoft Graph on behalf of the signed-in user.
Successful SCIM user provisioning
Microsoft Entra successfully provisioning the LedgerFlow user through SCIM.
Successful SCIM user deprovisioning
SCIM lifecycle validation showing successful removal of active access through deprovisioning.
Outcome

Authentication, authorization, federation, and provisioning in one identity architecture.

IAM-02 demonstrates how modern enterprise applications integrate with Microsoft Entra across the full identity stack. The project combines SAML federation, custom claims, OpenID Connect authentication, OAuth delegated authorization, Microsoft Graph, and SCIM lifecycle provisioning while preserving real troubleshooting evidence from the implementation.