IAM-01 · Autumn Solutions

Zero Trust Identity Security

I designed and validated a layered Microsoft Entra identity security architecture using Conditional Access, phishing-resistant MFA, Identity Protection, Privileged Identity Management, emergency access, and legacy authentication controls.

5
Conditional Access controls
2
Emergency access accounts
1
Hardened PIM workflow
21
Technical evidence captures
Video Walkthrough · 2–3 min

See the project in action

A concise walkthrough of the architecture, Microsoft Entra configuration, security controls, and validation evidence behind this project.

Open on YouTube ↗
01 / Challenge

Reduce identity risk without creating a single point of failure.

Autumn Solutions needed stronger identity controls for workforce and privileged access while preserving emergency administrator access. The design needed to enforce Zero Trust principles without locking out recovery accounts or deploying untested controls directly into production.

Microsoft Entra ID Conditional Access Identity Protection PIM Phishing-Resistant MFA Zero Trust Emergency Access
02 / Architecture

Layered identity controls with staged validation.

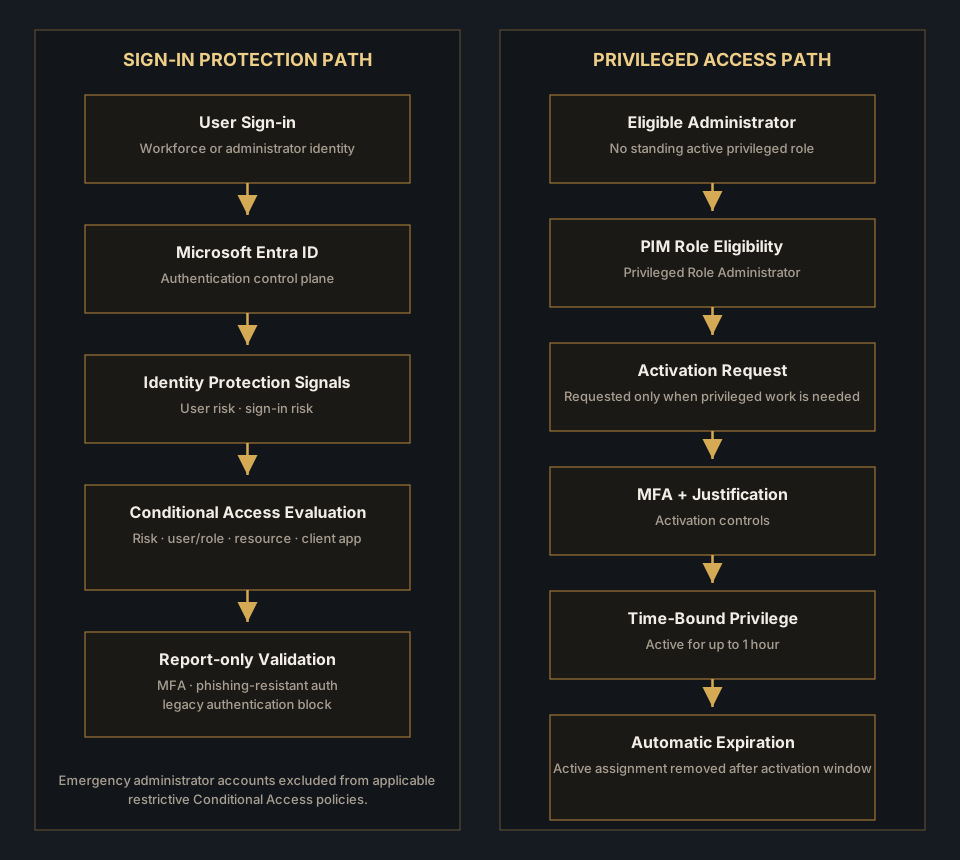
Conditional Access policies were designed around user context, authentication strength, identity risk, privileged access, and legacy protocol exposure. Controls were validated with pilot targeting, report-only deployment, What If analysis, and sign-in evidence before enforcement decisions.

IAM-01 Microsoft Entra Zero Trust identity architecture showing Conditional Access and Identity Protection separately from the PIM privileged activation lifecycle
03 / Security Controls

Defense in depth across authentication, risk, and privilege.

01

Staged MFA Enforcement

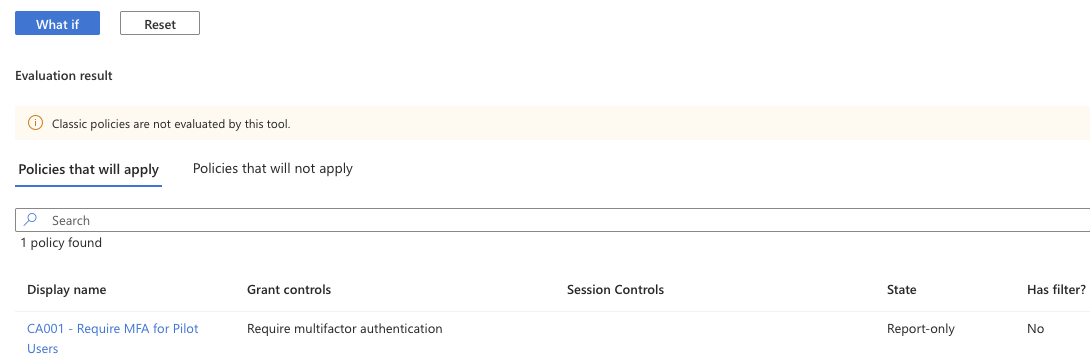
Built an MFA Conditional Access policy using a dedicated pilot group, report-only deployment, What If validation, and sign-in evidence before broader enforcement.

02

Phishing-Resistant Admin MFA

Applied stronger authentication requirements to privileged administrators using phishing-resistant authentication strength instead of relying only on standard MFA.

03

Risk-Based Sign-In Protection

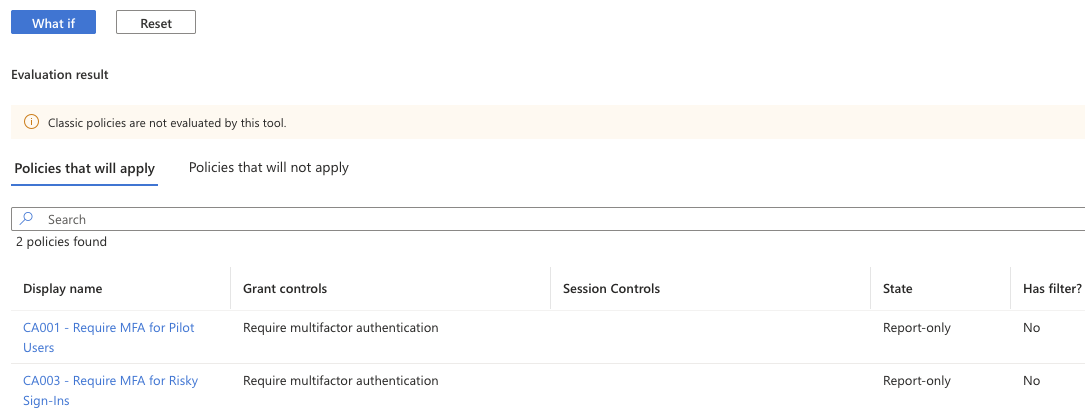
Configured Conditional Access to respond to risky sign-ins with an MFA requirement and validated the decision path using Entra What If analysis.

04

Risky User Remediation

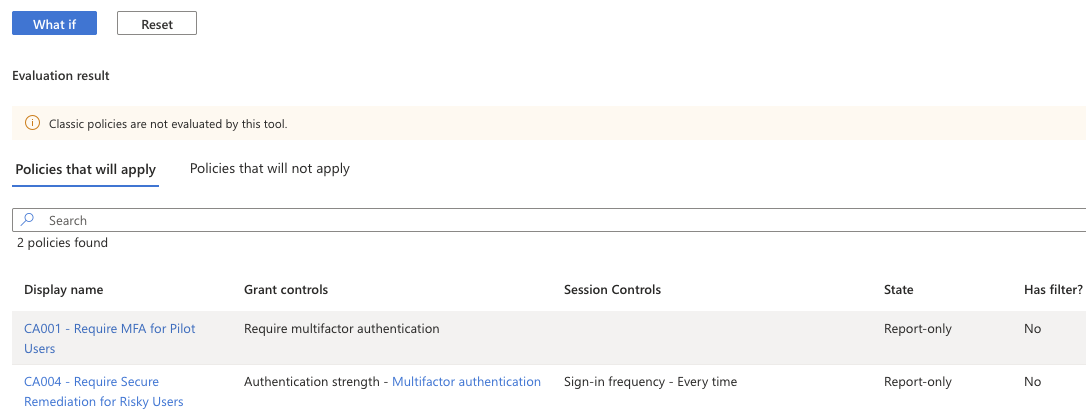
Added identity-risk controls for compromised-user scenarios so remediation requirements are driven by user risk rather than static access rules alone.

05

Privileged Identity Management

Hardened privileged role activation through Microsoft Entra PIM with activation requirements and auditable time-bound elevation instead of permanent administrative access.

06

Legacy Authentication Blocking

Designed a Conditional Access control to block legacy authentication protocols that cannot satisfy modern MFA and Zero Trust requirements.

04 / Resilience

Emergency access remained protected from accidental lockout.

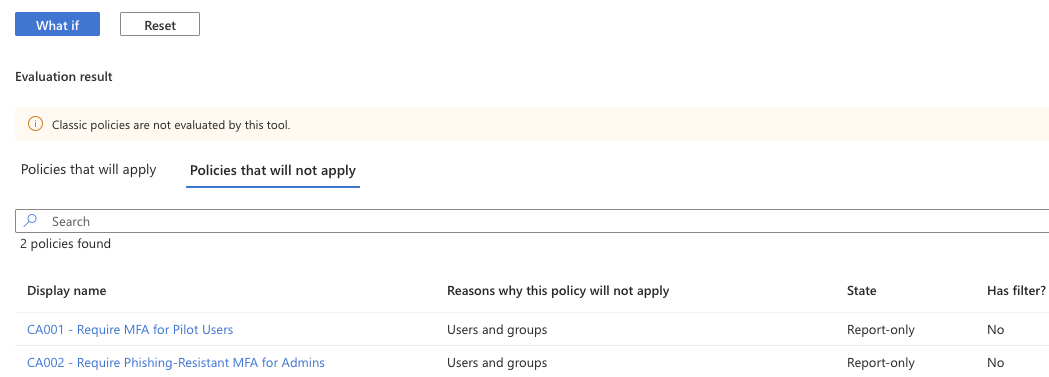
Two dedicated emergency Global Administrator accounts were intentionally excluded from applicable Conditional Access policies. The exclusions were validated rather than assumed, preserving a recovery path if normal authentication controls become unavailable.

Break-Glass Design

Emergency accounts were treated as a resilience control, not as ordinary administrator identities.

  • Dedicated emergency Global Administrator identities
  • Explicit Conditional Access exclusions
  • What If validation of exclusion behavior
  • Separate treatment from everyday privileged accounts
  • Protection against administrator lockout scenarios
05 / Evidence

Control validation across the Zero Trust identity stack.

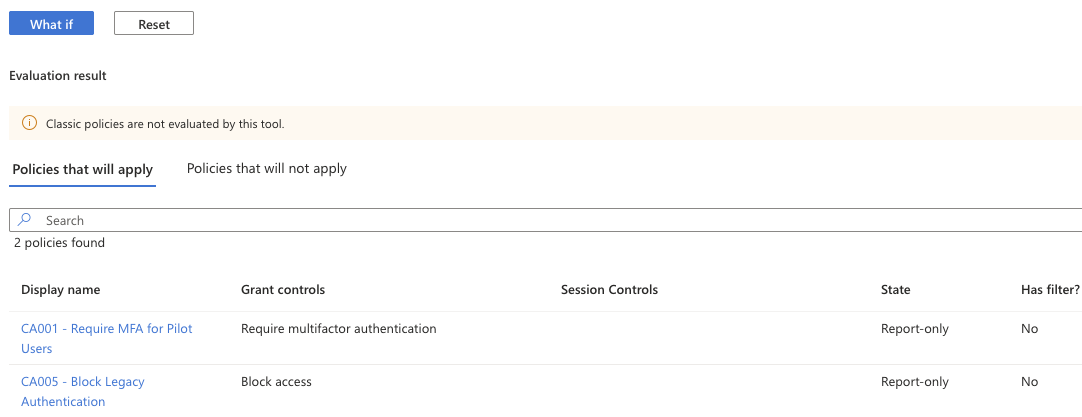
Conditional Access MFA What If validation
What If analysis validating the staged MFA Conditional Access decision before enforcement.
Emergency access Conditional Access exclusion validation
Validation that emergency access accounts remain excluded from the privileged authentication policy.
Risky sign in Conditional Access validation
Risk-based Conditional Access validation for risky sign-in scenarios.
Risky user Conditional Access validation
Identity Protection and Conditional Access validation for elevated user risk.
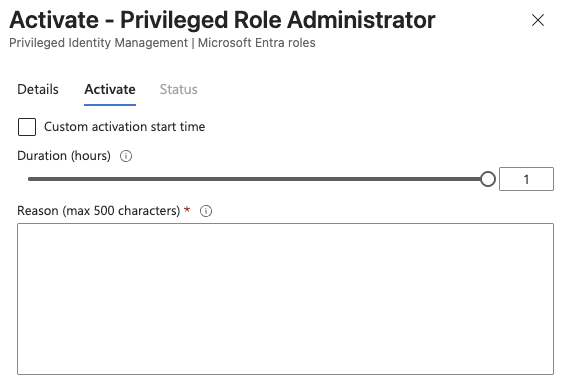
Microsoft Entra PIM privileged role activation
Hardened privileged role activation through Microsoft Entra Privileged Identity Management.
Conditional Access legacy authentication block validation
What If validation confirming the legacy authentication blocking policy decision.
Outcome

A layered Zero Trust identity control plane.

The final architecture combines staged MFA deployment, phishing-resistant authentication for administrators, risk-based identity protection, time-bound privileged access, emergency access resilience, and legacy authentication blocking. Controls were validated before enforcement so the project demonstrates not only how to configure Microsoft Entra security, but how to deploy it safely.